
MDR Cybersecurity: How Managed Detection And Response Works In Modern Networks

MDR: Operational Models, Staffing, and Performance Metrics
MDR services can be delivered through several operational models, including fully managed services, co-managed arrangements, or advisory support for in-house teams. In fully managed models, the service provider handles monitoring, investigation, and response actions according to pre-agreed processes. Co-managed models allow internal teams to retain operational control while receiving analyst support. Each model may suit different organisational risk profiles, resource availability, and compliance needs, and choices often balance control with access to specialist expertise.
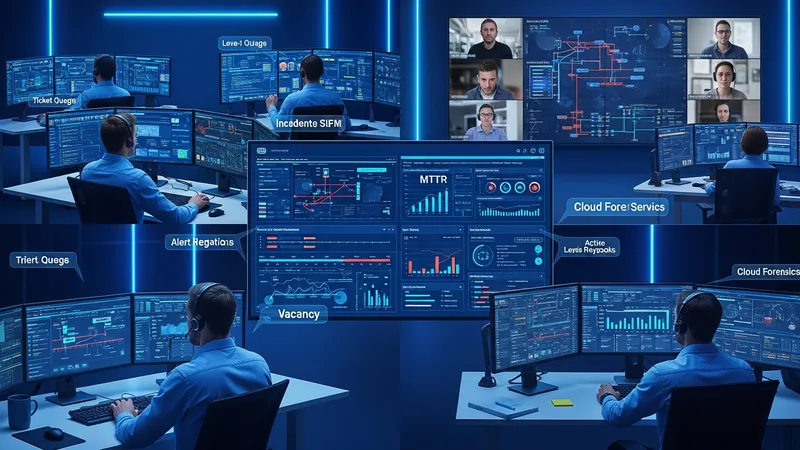
Staffing and skill composition in MDR operations normally include level-1 triage analysts, level-2 investigators, and senior threat hunters or incident responders. Access to specialised skill sets such as malware analysis, cloud forensics, or threat hunting is often cited as a reason organisations engage external MDR capabilities. Workforce constraints and retention challenges mean that some organisations may prefer managed or co-managed models to supplement internal capability gaps without committing to long-term hiring in specialist roles.
Performance metrics commonly used to evaluate MDR effectiveness include mean time to detect (MTTD), mean time to respond (MTTR), and the rate of confirmed incidents versus total alerts. These metrics may be presented as ranges or trends rather than absolute targets, and organisations often track them alongside contextual measures such as asset criticality and incident severity. Regular reviews of these metrics can inform tuning of detection logic, staffing adjustments, or shifts in the operational model to better align with changing threat patterns.
Contractual and compliance considerations often influence MDR arrangements. Service level agreements (SLAs) may define expected response windows for different severity levels, reporting cadences, and data handling obligations. Organisations also consider regulatory requirements for data sharing and breach notification when selecting operational approaches. Reviewing contractual terms and aligning them with internal incident response plans helps ensure that MDR collaboration supports regulatory and governance needs without creating ambiguity in roles or responsibilities.