
Coro Cyber Security: Overview Of Integrated Cyber Protection For Modern Workplaces

Data protection and identity controls in integrated workplace security
Data protection and identity controls are complementary areas within integrated security. Identity controls address who is accessing resources and under what conditions, using techniques such as multifactor authentication, conditional access, and session monitoring. Data protection focuses on classifying, labeling, and enforcing handling rules for sensitive content across endpoints, email, and cloud storage. When identity signals inform data policies, access can be adapted based on user risk, device posture, or location to reduce exposure of sensitive assets while maintaining business workflows.
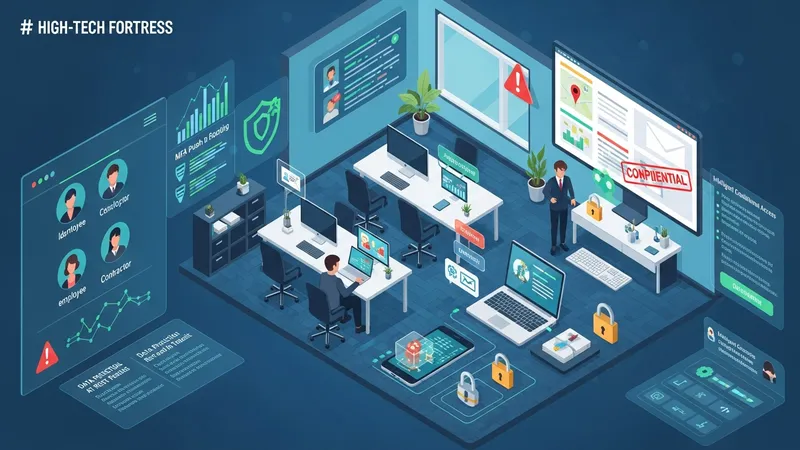
Common implementations map data classification to access and sharing controls so that labeled content triggers specific restrictions or encryption. For example, a file tagged as confidential may be blocked from sharing with external domains or require additional authentication for download. Identity-aware policies may throttle session capabilities or require step-up authentication for risky requests. These combined controls generally aim to limit unnecessary data exposure and to provide audit trails for compliance and incident review.
Integration challenges often include consistent classification across disparate storage systems and maintaining synchronized identity attributes across directories and cloud providers. Organizations typically use connectors and automated scanning to discover sensitive content and to apply labels consistently. Identity synchronization and governance processes help ensure that user attributes used in policy decisions are current, reducing false positives and avoiding overly restrictive access that could impede productivity.
Privacy and legal considerations shape how data protection and identity information are stored and used. Role-based access to logs, data minimization practices, and data retention schedules are common governance controls. Security teams often work with legal and compliance stakeholders to define acceptable retention and to ensure that monitoring practices align with applicable laws and internal policies. Clear documentation of these practices supports auditability and helps balance security monitoring with privacy obligations.